An AWS SCP (service control policy) is an AWS Organizations policy that sets the maximum permissions available to IAM users and roles in your member accounts. It grants nothing on its own: an identity-based or resource-based policy still has to allow the action, and the SCP caps how far those policies can reach.
Quick answer
- An SCP sets maximum permissions for principals in member accounts and grants none.
- An action needs an Allow from an SCP at every level from the root to the account, and a Deny at any level wins.
- The management account and service-linked roles are exempt. Root users of member accounts are not.
- Since May 15, 2026 you can attach 10 SCPs to each root, OU or account, and each SCP can hold 10,240 characters.
- For copy-paste policies, use the AWS SCP examples. For tree design, use the organizational unit design guide.
The sections below take you from the evaluation rule to a tested first SCP, and from an Access Denied error to the policy that caused it.
What is an AWS SCP?
SCPs in AWS Organizations are one of its policy types, available only in an organization with all features enabled. You attach an SCP to the root, an OU or an account, and it limits what IAM users and roles in the member accounts below can do, root user included. If an SCP blocks a permission, nobody in that account can use it, even with the AdministratorAccess IAM policy.
How SCPs differ from IAM policies
| Aspect | Service Control Policies (SCPs) | IAM Policies |
|---|---|---|
| Scope | Attached to the organization root, an OU, or an account | Attached to IAM users, groups, and roles (or to resources) |
| Purpose | Define maximum permissions (permission guardrails) | Grant or deny specific permissions |
| Management Account | Does not affect the management account | Applies to all users/roles including in management account |
| Hierarchy | Every level from root to account must allow; a Deny anywhere wins | No hierarchy, must be explicitly attached |
| Service-Linked Roles | Does not affect service-linked roles | Can't edit service-linked role permissions; only control who creates or deletes the role and edits its description |
| Effect | Limits what is possible to do | Grants what you can do |
How SCPs combine with other policies
AWS defines effective permissions as the logical intersection between what SCPs and resource control policies (RCPs) allow and what identity-based and resource-based policies allow. SCPs cap principals, RCPs cap resources, and identity-based and resource-based policies grant the actual access.
Within one account, identity-based and resource-based policies form a union, so an allow in either is enough. SCPs and RCPs sit on top of that union as a ceiling, and an explicit deny in any of them wins. A local IAM administrator can't grant their way past it.
Why teams use SCPs
Across many accounts, keeping guardrails consistent through IAM alone stops scaling: each account has its own administrators, and any of them can widen a policy. Get the IAM fundamentals right in each account first, then use SCPs for the guardrails nobody inside an account should remove:
- Security: Block public S3 buckets, require encryption, prevent disabling CloudTrail
- Cost: Restrict expensive EC2 instance types, limit services to approved Regions
- Compliance: Keep workloads in approved Regions, protect audit logging
- Critical resources: Prevent deletion of security services and production workloads
If developers launch r5.24xlarge instances for tests, one SCP that denies anything outside approved instance families stops that in every development account at once.
SCPs and organizational units
An organizational unit (OU) is a container for accounts, and OUs can nest. An account is subject to every SCP on its path up to the root.
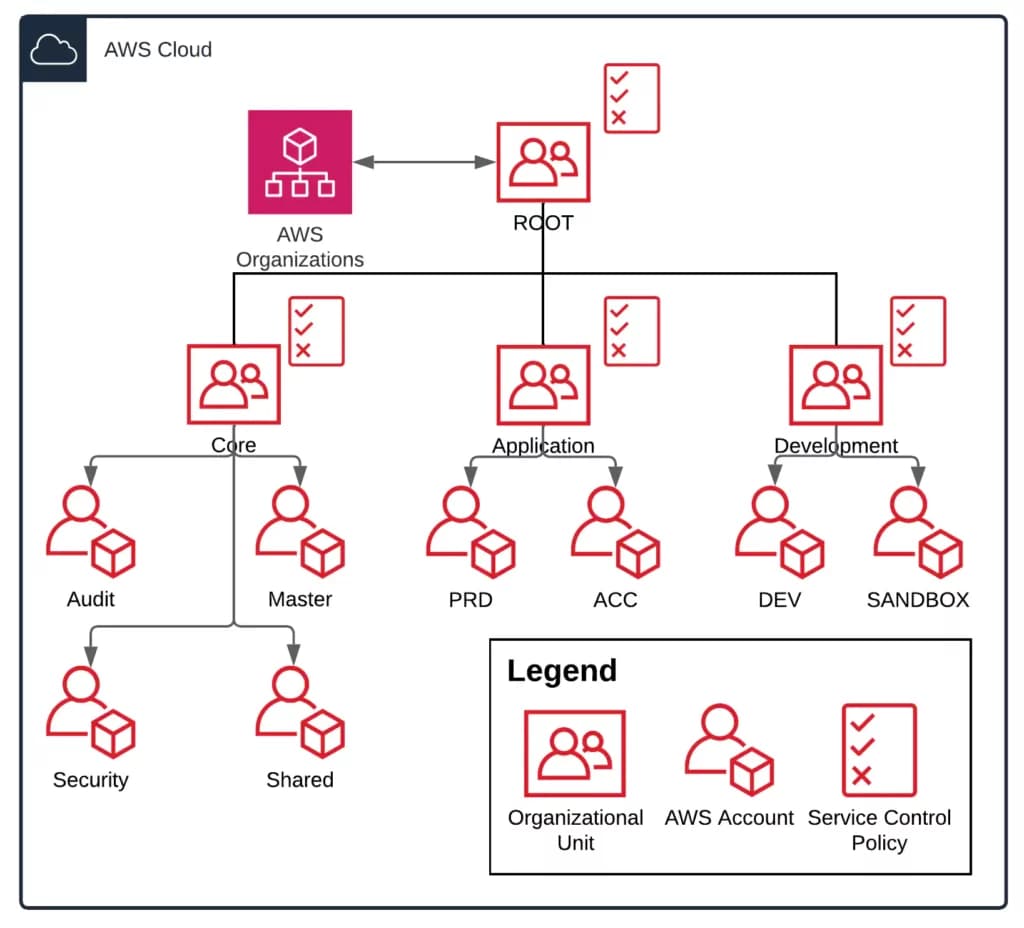
AWS Organizations account setup with OU and SCPs
Here the Application OU holds strictly controlled production and acceptance accounts, while the Development OU gives sandboxes more room. The OU guide shows how SCPs flow down an OU tree with a level-by-level example. The SCP-specific rule of thumb: attach shared guardrails high in the tree, test new SCPs in a staging OU, and keep nesting shallow so a denied request has fewer levels to trace.
How SCP evaluation works
An action is allowed in a member account only if an SCP allows it at every level from the root to the account, and it's denied if any SCP on that path denies it. The SCP evaluation rules require "an explicit Allow statement at every level from the root through each OU in the direct path to the account (including the target account itself)." Anything not explicitly allowed is denied.
- FullAWSAccess supplies the Allow. When you enable SCPs, Organizations attaches this AWS managed policy at the root, each OU and each account. Remove it at any level without a replacement and every OU and account below that level is blocked from all actions.
- Allows filter, they don't add. An Allow lower in the tree can't restore what a higher level didn't allow. Replace FullAWSAccess at the root with an allow list and that list restricts everything beneath, even OUs that keep FullAWSAccess.
- A Deny anywhere wins. A Deny at the root beats Allows at the OU and account, and no IAM policy can override it.
- Inherited SCPs don't count against limits. The 10-per-node limit counts only SCPs attached directly. Each root, OU and account must keep at least one SCP attached.
The failure I'd watch for: someone detaches FullAWSAccess from a Workloads OU to "tighten" it and leaves only a Deny policy. Every account under Workloads now fails every call with "no service control policy allows."
What SCPs do not restrict
SCPs don't affect:
- The management account. Keep workloads out of it and use it for organization management.
- Service-linked roles. AWS services use them, and SCPs can't restrict them.
- Principals outside your organization. Your SCP doesn't stop a user in another account who reaches your S3 bucket through a bucket policy. RCPs close that gap for supported services.
SCPs do restrict the root user of every member account, and they apply to member accounts registered as a delegated administrator. AWS lists a few more exempt tasks, such as registering for Enterprise Support as the root user, on the SCP reference page.
SCP vs RCP vs declarative policies
SCPs limit principals, RCPs limit resources, and declarative policies pin service configuration. AWS added RCPs in November 2024 and declarative policies on December 1, 2024. Both work alongside SCPs rather than replacing them:
| SCP | RCP | Declarative policy | |
|---|---|---|---|
| Controls | Maximum permissions of IAM users and roles in member accounts | Maximum permissions on resources in member accounts, whoever calls | Service configuration baselines, enforced in the service's control plane |
| Doesn't cover | Management account, service-linked roles, outside principals | Management account, service-linked roles, AWS managed KMS keys, unsupported services | API authorization; it does govern service-linked roles |
| Attached per node | 10 | 5 (RCPFullAWSAccess counts toward them) | 10 |
| Max size | 10,240 characters | 5,120 characters | 10,000 characters |
| Use it when | You limit what your own identities can do | You stop external principals reaching your resources (data perimeter) | A setting such as VPC Block Public Access or allowed AMIs must hold, even when new APIs ship |
RCPs cover a growing list of supported services, so check it before you rely on one. Declarative policies launched for EC2, EBS and VPC settings and now cover more services. For most organizations, SCPs come first, then RCPs once you build a data perimeter.
What changed for AWS SCPs in 2025 and 2026
The SCP you wrote two years ago still works, but four changes affect how you write and debug new ones:
- September 19, 2025: full IAM policy language. SCP Allow statements now support conditions, individual resource ARNs and
NotAction, and any statement can useNotResourceand wildcards at the beginning or middle of Action strings.PrincipalandNotPrincipalremain unsupported. - January 21, 2026: policy ARNs in Access Denied messages for same-account and same-organization requests, rolling out gradually across services.
- May 15, 2026: higher SCP quotas. Attachments per root, OU or account went from 5 to 10, and maximum size from 5,120 to 10,240 characters. No action needed.
- July 30, 2026: the IAM policy simulator moved into the IAM console and can now test SCPs.
Conditions in Deny statements always worked, so for a deny-list setup the practical gains are NotResource and mid-string wildcards. The new Allow features matter once you replace FullAWSAccess (see the conditions section below). If the SCP syntax reference still says Allow statements only accept "*" as the Resource, the launch announcement is the newer source.
Create your first SCP
This walkthrough enables SCPs, creates one Deny policy and attaches it to a test OU.
Prerequisites
- An organization with All features enabled. In the AWS Organizations Console, choose Create an organization; the AWS Organizations setup guide covers the rest.
- Sign-in access to the management account.
- A non-critical account you can move into a test OU.
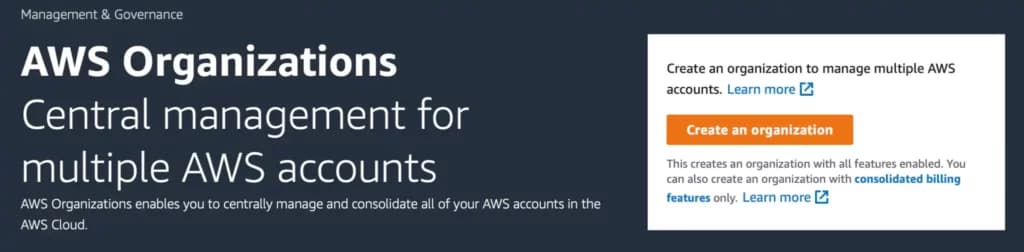
AWS Console: create an AWS Organization
Your organization structure is where you create OUs and group accounts.
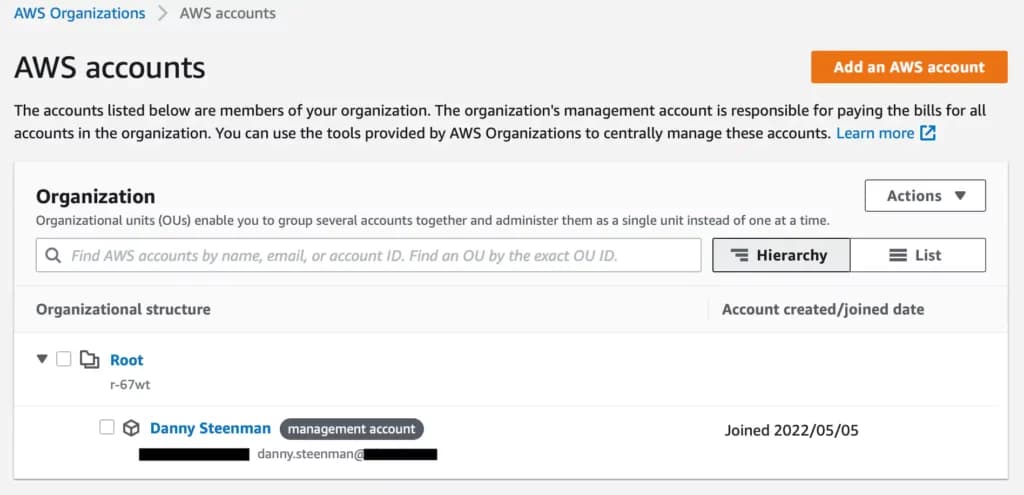
AWS console: AWS Organizations organizational structure
Enable service control policies
SCPs are a policy type you enable explicitly. Go to the Service Control Policies page and click Enable service control policies.
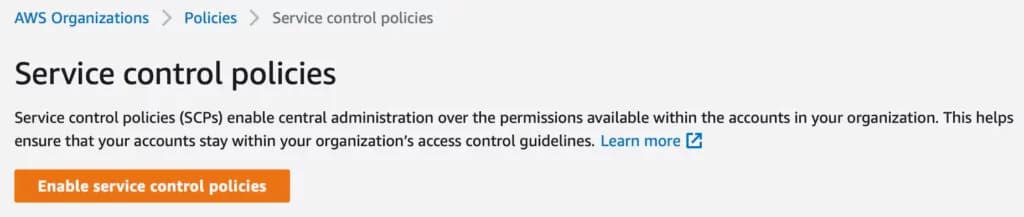
AWS console: AWS Organizations enable Service Control Policy
Organizations then attaches the AWS managed FullAWSAccess policy at the root and at every OU and account.
Understanding the FullAWSAccess policy
The FullAWSAccess policy is managed by AWS and allows every action:
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Effect": "Allow",
      "Action": "*",
      "Resource": "*"
    }
  ]
}
Keep FullAWSAccess, or another Allow, attached at every level. Your guardrails go on top as Deny statements.
Create your first SCP: prevent organization departure
A common first SCP stops member accounts from leaving the organization, so nobody can step outside central governance.
From the Service Control Policies page, click Create policy.
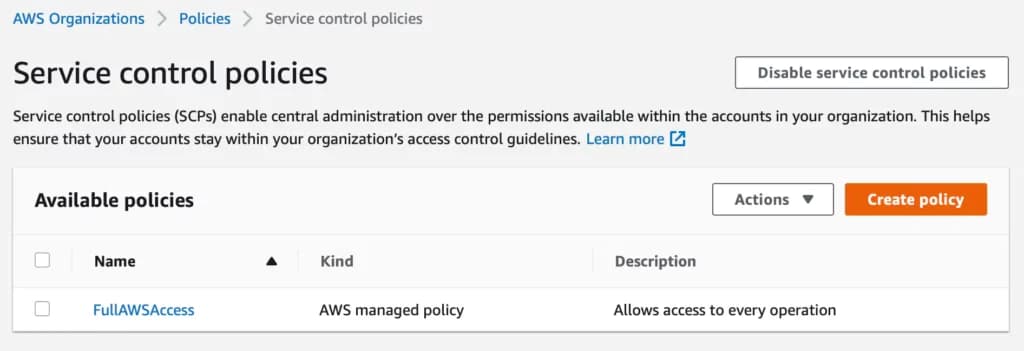
AWS console: AWS Organizations create new Service Control Policy
Add a policy name, description, and the following JSON:
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Sid": "PreventOrganizationDeparture",
      "Effect": "Deny",
      "Action": "organizations:LeaveOrganization",
      "Resource": "*"
    }
  ]
}
Click Create policy to save it.
Attach the SCP to a test OU
Creating an SCP doesn't activate it. You must attach it to an OU or account.
Create a dedicated test OU first. Never attach untested SCPs directly to your root or production OUs.
- Go to the Targets tab of your newly created policy
- Click Attach
- Select your test OU or a non-critical account
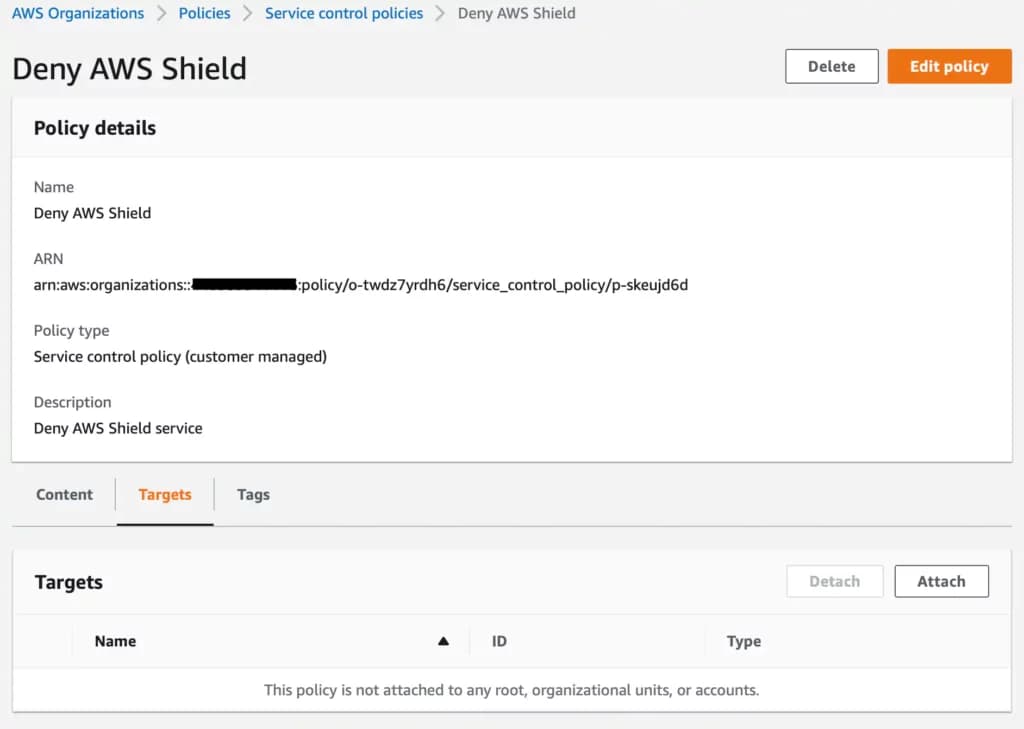
AWS console: AWS Organizations Service Control Policy rule target tab
Once attached, any IAM user or role in accounts under that OU, root user included, is denied organizations:LeaveOrganization.
Validate the SCP
Confirm the SCP works before you expand it:
- Check the policy's Targets tab lists only the test OU
- In the IAM policy simulator, which now evaluates SCPs, simulate
organizations:LeaveOrganizationfor a role in the test account and expect a deny - After real work hits the SCP, find denied calls in CloudTrail in US East (N. Virginia), where Organizations records its events, and check the
errorMessagesays "with an explicit deny in a service control policy"
Don't test this SCP with a live LeaveOrganization call: if it isn't attached where you think, the account can actually leave.
Worked AWS SCP example: restrict Regions
Region restriction is one of the most common SCPs, for data residency and a smaller attack surface.
This version is based on the Control Tower Region deny control, trimmed to a subset of its global-service exemptions:
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Sid": "DenyAllOutsideApprovedRegions",
      "Effect": "Deny",
      "NotAction": [
        "a4b:*",
        "account:*",
        "acm:*",
        "aws-marketplace-management:*",
        "aws-marketplace:*",
        "aws-portal:*",
        "billing:*",
        "budgets:*",
        "ce:*",
        "chime:*",
        "cloudfront:*",
        "config:*",
        "cur:*",
        "directconnect:*",
        "ec2:DescribeRegions",
        "ec2:DescribeTransitGateways",
        "ec2:DescribeVpnGateways",
        "fms:*",
        "globalaccelerator:*",
        "health:*",
        "iam:*",
        "importexport:*",
        "kms:*",
        "mobileanalytics:*",
        "networkmanager:*",
        "organizations:*",
        "pricing:*",
        "route53:*",
        "route53domains:*",
        "s3:GetAccountPublicAccessBlock",
        "s3:ListAllMyBuckets",
        "s3:PutAccountPublicAccessBlock",
        "shield:*",
        "sso:*",
        "sts:*",
        "support:*",
        "trustedadvisor:*",
        "waf-regional:*",
        "waf:*",
        "wafv2:*"
      ],
      "Resource": "*",
      "Condition": {
        "StringNotEquals": {
          "aws:RequestedRegion": [
            "eu-west-1",
            "eu-central-1"
          ]
        }
      }
    }
  ]
}
Gotchas:
- Global services must be exempted through
NotActionor they're blocked entirely. AWS's minimal example exempts only CloudFront, IAM, Route 53 and Support. The Control Tower list is longer and changes over time, so compare against it before you deploy. - Amazon Bedrock global cross-Region inference sends
aws:RequestedRegionasunspecified. If you use it, addunspecifiedto the approved Regions or exempt inference profiles with thebedrock:InferenceProfileArncondition, as the Bedrock guide shows. - Test in a sandbox account first, because it can block legitimate operations.
Two other common first SCPs, both with ready-to-use JSON in the SCP examples by OU:
- Require MFA for sensitive IAM operations. Deny high-impact IAM actions when
aws:MultiFactorAuthPresentis false. Scope it to roles that humans use. - Restrict development instance types. Deny
ec2:RunInstancesoutside approved families to keep test spend predictable.
Testing and rollout
Never attach untested SCPs to your root or production accounts. A misconfigured SCP can break operations across the organization.
Test in a dedicated OU
- Create an OU called
SCP-Testing, or a Policy Staging OU - Move a non-critical sandbox account into it
- Confirm
FullAWSAccess(or another Allow) is attached at the root, the test OU and the account - Attach your new SCP to the test OU
Roll out in stages
Then roll out from lowest to highest risk:
- Sandbox/Development accounts
- Staging/Pre-production accounts
- Production accounts, last
Move one account at a time and watch denials across the team's normal deploy and batch cycles before the next. Tell account owners what changes and when.
Find SCP denials in CloudTrail
With Athena, search for error messages that name a service control policy (in CloudTrail Lake, replace cloudtrail_logs with your event data store ID):
SELECT
  eventTime,
  eventName,
  userIdentity.arn,
  errorCode,
  errorMessage
FROM cloudtrail_logs
WHERE errorMessage LIKE '%service control policy%'
ORDER BY eventTime DESC
Check what's in use before you deny it
From the management account, the Organization activity page in the IAM console (or the GenerateOrganizationsAccessReport API) shows service last accessed data for the root, an OU, an account or an SCP. It counts failed attempts too, so confirm recent use in CloudTrail before blocking a service.
Validate with IAM Access Analyzer
IAM Access Analyzer policy validation accepts SCPs as a policy type and flags grammar errors and best-practice issues at no extra charge. AWS also suggests custom policy checks (a paid feature) for SCPs, but their check APIs list only identity and resource policy types. Don't count on them for SCP changes yet; review the SCP diff in your pull request instead.
Roll back
Detach the SCP from the affected OU or account, or edit out the offending statement (an edit applies to every target at once). Keep both steps in a runbook and rehearse them once.
Troubleshooting SCP Access Denied errors
One of the most common questions I hear is: "Why am I getting Access Denied when my IAM policy clearly allows this action?"
The usual suspects are SCPs, RCPs, resource-based policies and permissions boundaries, and the error message usually names the policy type.
Read the error message first
An explicit Deny looks like this, with the policy ARN appended in same-account and same-organization cases where the service supports it:
User: arn:aws:iam::123456789012:user/John is not authorized to perform: codecommit:ListRepositories with an explicit deny in a service control policy: arn:aws:organizations::777788889999:policy/o-exampleorgid/service_control_policy/p-examplepolicyid123
A missing Allow ends with "because no service control policy allows the codecommit:ListRepositories action" instead. That points at a level on the path with no Allow, usually a missing FullAWSAccess. Some services don't use this format, and when several policy types deny a request, the message names only one.
Common SCP denial scenarios
Scenario 1: IAM policy allows an action, but an SCP denies it.
- Solution: Narrow the SCP, or move the account to an OU with the guardrails it needs
Scenario 2: A Region restriction SCP blocks a global service.
- Solution: Add the service's actions to the
NotActionlist
Scenario 3: FullAWSAccess was detached from one OU without a replacement, like the Workloads OU case above.
- Solution: Reattach
FullAWSAccess, or an allow list, at that level
Debugging SCP vs IAM vs resource policy conflicts
- Read the errorMessage: Does it mention "service control policy"? If yes, it's an SCP.
- Check the account: Is this the management account? If yes, it's not an SCP.
- Run the IAM policy simulator (below).
- Walk the path: Review the SCPs attached at the account, each parent OU and the root. Every level needs an Allow, and any Deny counts.
Test with the IAM policy simulator
Since July 2026 the simulator lives in the IAM console and tests SCPs together with identity-based policies, permissions boundaries and resource-based policies. Know its limits:
- It tells you whether an SCP allows or denies an action, but not which SCP statement matched.
- It doesn't evaluate RCPs.
- In the console you can only set condition keys that appear in non-SCP policies. To test an SCP condition such as
aws:RequestedRegion, supply its value through the CLI or API.
If the simulator says "allowed" but the real request fails, check RCPs and condition values the simulator didn't set.
Real-world example with solution
Problem: A developer can't launch an EC2 instance in us-west-2, but their IAM policy clearly allows ec2:RunInstances.
Debugging:
- Find the denied request in CloudTrail
- Error message: "with an explicit deny in a service control policy", followed by the policy ARN where available
- Open that policy: it's the Region SCP above, which permits only
eu-west-1andeu-central-1
Solution: Either:
- Add
us-west-2to the approved Regions in the SCP - Move the account to an OU with a different Region SCP
- Explain that
us-west-2is outside company policy
SCP design practices
After creating and testing hundreds of SCPs across different organizations, these are the patterns that work. For organization-wide guidance beyond SCPs, see AWS Organizations best practices.
Deny-list vs allow-list strategy
SCPs can be configured as either:
- Deny-List: Actions are allowed by default (via
FullAWSAccess), and you explicitly deny specific actions - Allow-List: You replace
FullAWSAccesswith policies that allow only listed services
Best practice: Use deny-list for most organizations.
Why? With a deny list, new AWS services are available unless you block them. With an allow list, new services stay blocked until you allow them, so every launch your teams want means an SCP change. Highly regulated environments may want exactly that; if so, assign a team to watch AWS What's New.
Use explicit Deny statements
The AWS Security Blog post on full IAM language in SCPs recommends explicit Deny statements in most cases, and one broad Allow with multiple targeted Denies. Relying on Allows alone can lead to unintended access, because a broader Allow at the same level makes a narrower one meaningless.
A Deny wins at any level, and neither IAM policies nor lower-level SCPs can override it. The two snippets below are single statements; put them in your policy's Statement array.
{
  "Effect": "Deny",
  "Action": "s3:DeleteBucket",
  "Resource": "*"
}
Put conditions in Deny statements
Conditions in Allow statements are now supported, but with FullAWSAccess attached they restrict nothing. FullAWSAccess already satisfies that level's Allow, and AWS documents that an allow-list policy "has no effect" while the default Allow * is attached. Write the restriction as a Deny instead:
{
  "Sid": "DenyUnapprovedInstanceTypes",
  "Effect": "Deny",
  "Action": "ec2:RunInstances",
  "Resource": "arn:aws:ec2:*:*:instance/*",
  "Condition": {
    "StringNotLike": {
      "ec2:InstanceType": ["t3.*", "t3a.*", "m5.large"]
    }
  }
}
A conditional Allow only restricts once you've replaced FullAWSAccess at that level.
Assign owners and a review cadence
I'd review CloudTrail denials and new AWS services quarterly, audit every SCP yearly, and revisit them after any security incident. Record each SCP's owner in its description.
Keep a break-glass path
The management account is exempt from SCPs, so keep a break-glass identity there with MFA. Document the procedure, review every use, and test it yearly.
AWS SCP limits and quotas
These are the Organizations quotas as of November 2026. All policy limits are hard limits.
| Quota | Limit | Notes |
|---|---|---|
| SCPs attached per root, OU or account | 10 | Raised from 5 on May 15, 2026; direct attachments only; minimum 1 |
| Maximum SCP size | 10,240 characters | Raised from 5,120 on May 15, 2026 |
| SCPs per organization | 10,000 | |
| RCPs attached per node / size | 5 / 5,120 characters | RCPFullAWSAccess counts toward the 5 |
| RCPs per organization | 2,000 | Raised from 1,000 in July 2026 |
| OUs per organization | 2,000 | |
| OU nesting depth | Five levels of OUs under the root | |
| Accounts per organization | 10 by default | Adjustable through Service Quotas from the management account |
Policy size: The console removes extra whitespace before counting; the CLI and SDKs save the policy exactly as provided. If you deploy from a pipeline, minify the JSON at deploy time and keep the readable version in source control.
Attachment limit: Out of slots? Combine related Deny statements into one policy, or move a guardrail one level up if its sibling OUs and accounts should get it too, since inherited SCPs don't count.
SCPs in the broader governance setup
SCPs work best as one layer of a cloud foundation built on an AWS Landing Zone, defined in code rather than through ClickOps. Compare Control Tower alternatives on how they handle SCPs, and see AWS multi-account best practices for the account structure around them. Two neighbors matter most:
- IAM Identity Center: Permission sets grant access in member accounts; SCPs cap it. Test new SCPs by signing in to an affected account.
- Centralized logging: An organization trail delivering to a log archive account gives you one place to search for SCP denials.
Conclusion and next steps
An AWS SCP is the ceiling for every IAM principal in your member accounts. Keep an Allow at every level from root to account, put your guardrails in Deny statements, and remember that a Deny anywhere wins. Plan within 10 SCPs per node and 10,240 characters per policy, and add RCPs when you need to cap access from principals outside your organization.
Your next steps:
- Enable SCPs and confirm
FullAWSAccessis attached at every level - Ship the leave-organization SCP to a test OU and validate it in the policy simulator
- Add a Region restriction, checked against the current Control Tower list
- Pick further guardrails from the SCP examples library
- Plan RCPs once your SCP baseline is stable
Frequently Asked Questions
What is an SCP in AWS?
Does an SCP grant permissions?
Do SCPs apply to the management account?
What is the difference between an SCP and an IAM policy?
How many SCPs can you attach to an OU?
What is the difference between an SCP and an RCP?
Next step